
Single-file vault
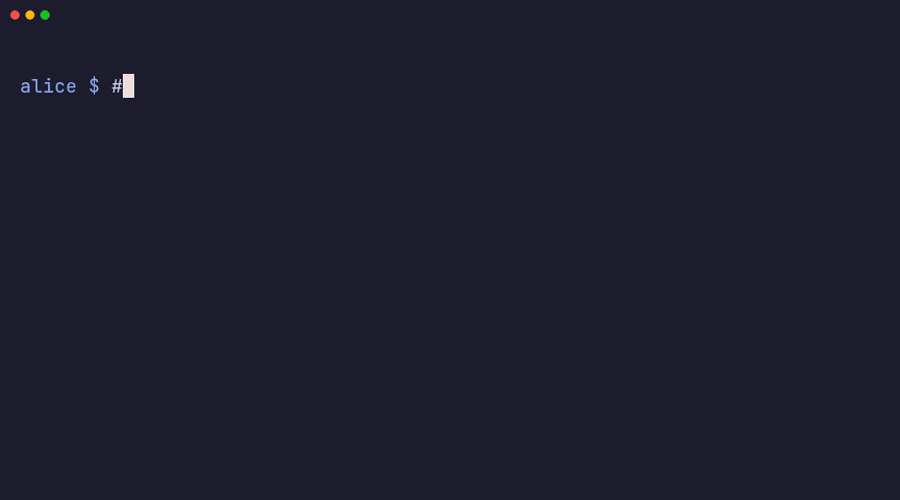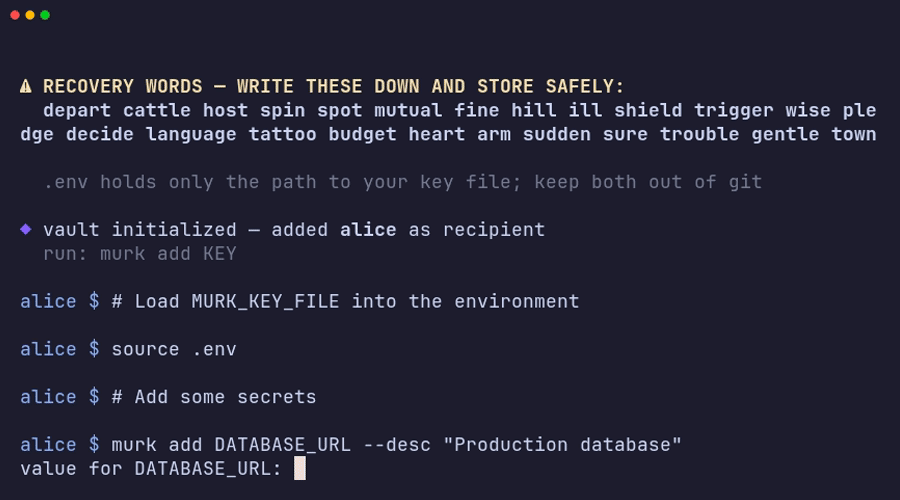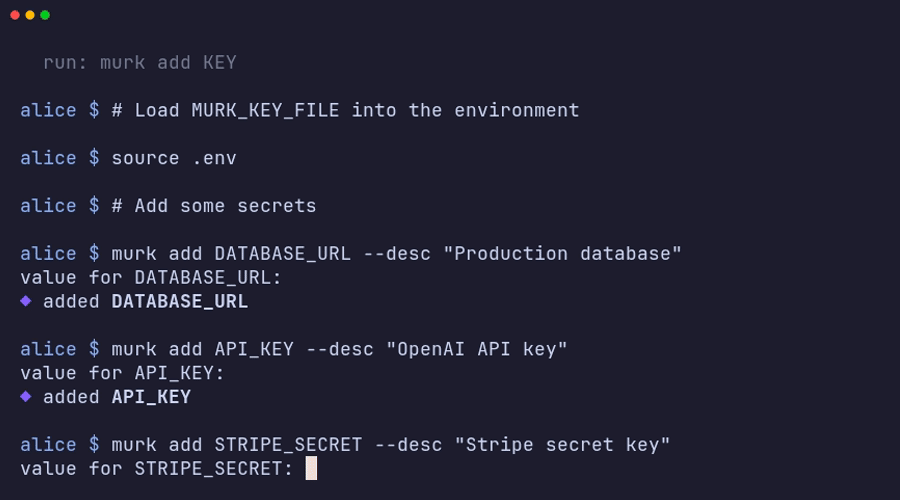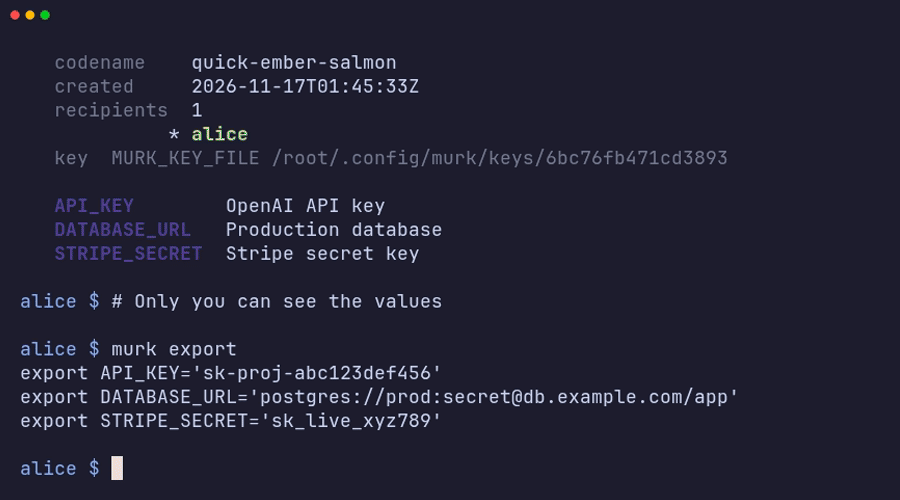
Encrypted secrets live in one .murk file, safe to commit. Values are
encrypted with age. Key names stay readable
so diffs stay meaningful.
.murk file in your repo. age encryption, readable key names, no server.Single-file vault
Encrypted secrets live in one .murk file, safe to commit. Values are
encrypted with age. Key names stay readable
so diffs stay meaningful.
Per-recipient encryption
Every teammate gets their own key. Add and revoke recipients with
murk circle. There is no shared vault password, but when someone leaves
you still rotate the secrets they could read.
Scoped agent access (experimental)
Give an AI agent a grant that reads only the secrets you name, through
murk agent exec or MCP. The agent receives those values in plaintext.
See AI agents & MCP.
Recover from a phrase
murk init prints 24 BIP39 recovery words for your age key. murk restore
turns them back into the key. No account, no reset email, no server. SSH
and hardware keys have no phrase.
Teams often share .env files over chat, which leaves secrets in message
history. Vault needs a server. SOPS supports more key backends than murk and
has more to configure.
murk is simple: one key on your machine, one encrypted file in your repo. See the threat model for what it protects and what it does not.
murk is pre-1.0 and has not been independently audited. Use good judgment with production secrets.
| murk | SOPS | Vault | dotenvx | git-crypt | |
|---|---|---|---|---|---|
| Encrypted values, readable keys | Yes | Yes | N/A | Yes | No (whole file) |
| Per-recipient encryption | Yes | Yes | ACL-based | No (shared key) | Yes (GPG) |
| Private per-user overrides | Yes | No | No | No | No |
| Requires a server | No | No | Yes | No | No |
| Cloud KMS required | No | Optional | Typically | No | No |
| Single binary, no runtime | Yes | Yes | Yes (needs a server) | Yes | Yes |
| Built-in direnv integration | Yes | No | No | Not documented | No |
| Recovery phrase | Yes (BIP39) | No | No | No | No |
Compared against each project’s documentation as of murk v0.14.0. Other tools change, so check their current docs.
SOPS is the closest alternative. Both encrypt values in place and support
age. murk adds private per-user values, a single-file vault, built-in team
management (murk circle) and BIP39 key recovery. SOPS supports more KMS
backends and has a larger ecosystem.
Vault solves a different problem. It is central infrastructure for secret storage, rotation and dynamic credentials. If you need a secrets server, use Vault. murk keeps encrypted secrets in a repo.
dotenvx encrypts .env files with one shared key for the whole team. It
has no per-recipient encryption, so when someone leaves, everyone needs a new
key.
git-crypt encrypts whole files through git filters. Its diffs are opaque. Revoking a team member is impractical without re-encrypting git history.
Not sure murk is the right fit? See Is murk right for you? for a situation-by-situation suitability matrix and the 0.x release contract.
To try it, install murk, then follow the quick start.